Introduction
Someone in a public Discord server posted about an “unsecured government satellite” on Censys. We followed the lead to a web application tied to a NOAA polar orbit ingestion system. Testing the application eventually led us to command injection.
The system was already being discussed in public, and the application looked old enough to warrant a closer look. We wanted to understand the exposure and report anything serious we found.
We did not have explicit written permission to test the system. We kept our testing narrow and limited the impact, stopping once we had enough evidence to report the issue. The relevant government body appeared to accept security reports.
Initial Reconnaissance
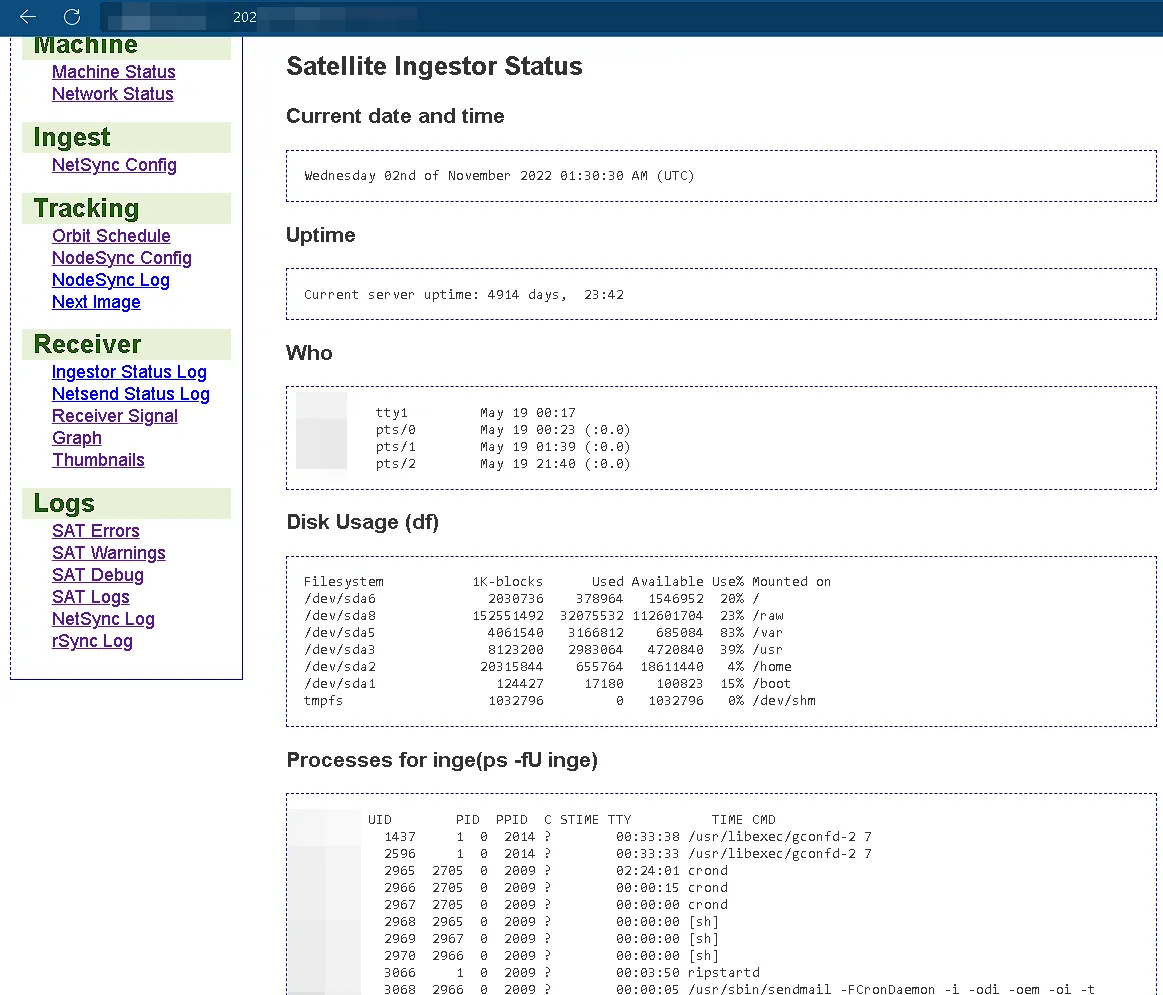
The web application displayed details about the underlying system. We wanted to know where that data came from and how the server fetched it. The information on the page gave us a starting point for testing the application’s parameters.
Discovery
While testing the application’s parameters, we found one called f. Our initial tests showed it could include local files from the web server.
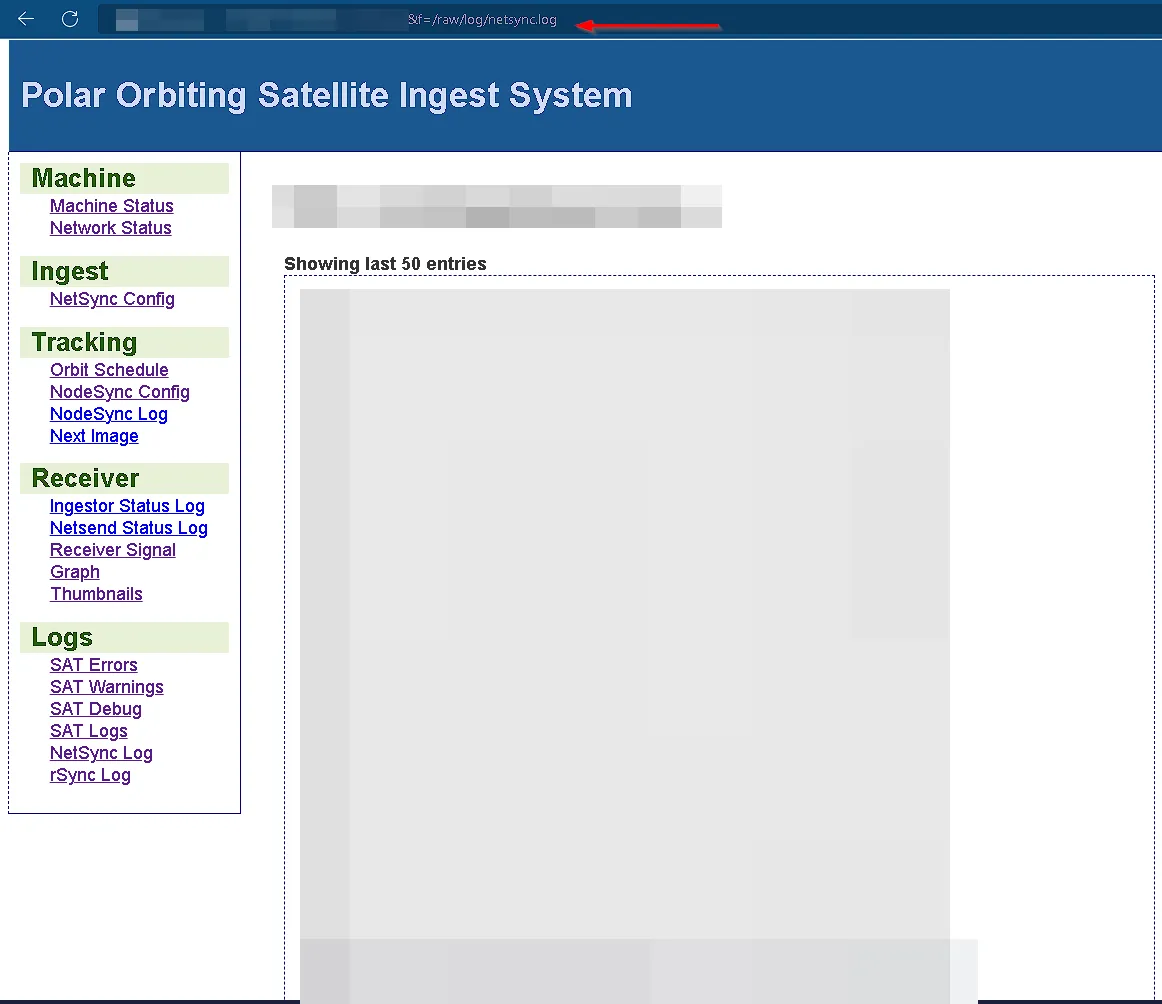
The file associated with that parameter kept updating. It looked as though a process on the server was producing the data in real time.
The backend ran PHP on Apache. We considered how it might be handling the parameter. file_get_contents() could explain a file read and might expose path traversal or server-side request forgery (SSRF).
An include() call would also explain local file inclusion (LFI), with possible routes to code execution such as log poisoning.
We also tested whether the application passed the input to a system call such as exec(), system(), or shell_exec(). Shell metacharacters including ; and && let us break out of the intended command and run our own.
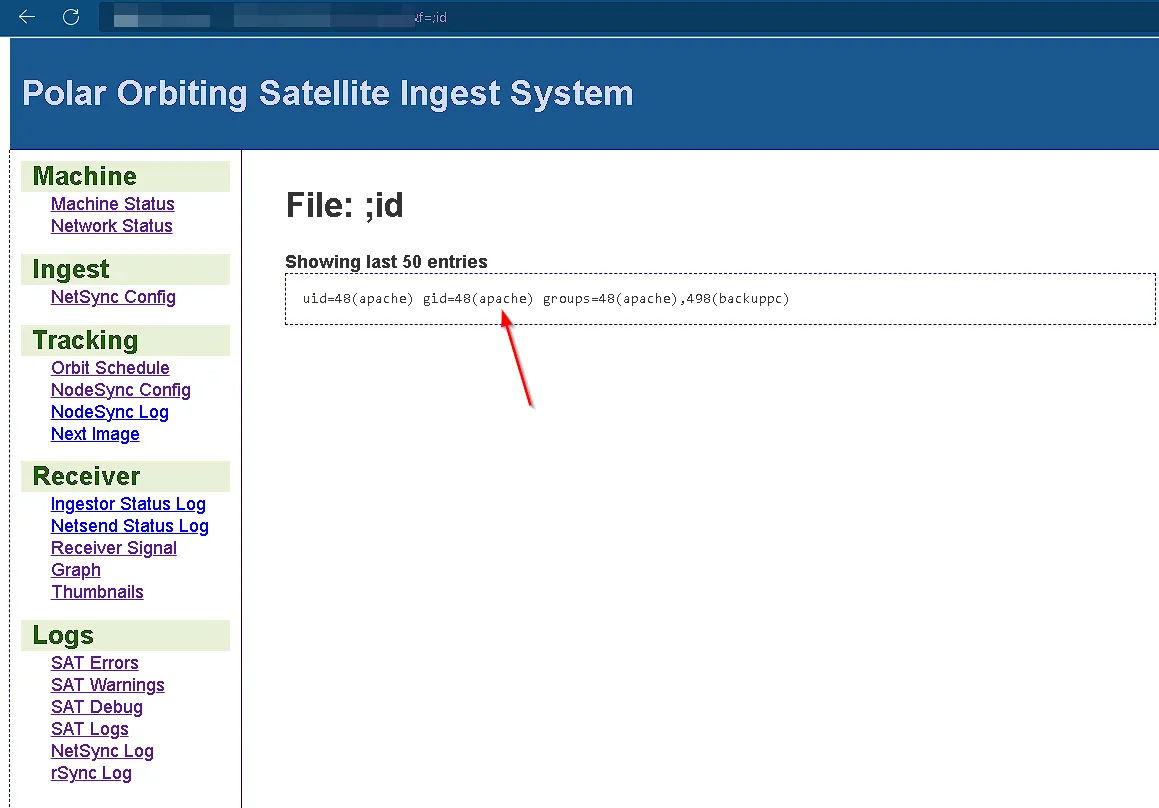
That confirmed command injection.
Responsible Disclosure
Once we had confirmed the impact, we stopped testing and prepared a disclosure.
The report included the steps to reproduce the injection, the potential impact, and recommendations for a fix.
Our initial contact with the relevant government body was made on October 28th, 2022, at 11:23 AM. We received a prompt and professional response on November 24th, 2022. The agency took the findings seriously and later confirmed that the issue had been patched.
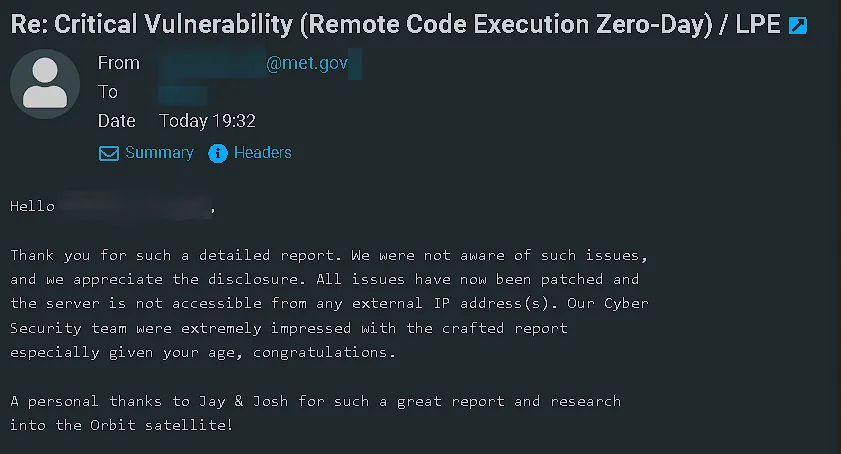
Conclusion: From Discovery to the BSides Cymru Stage
The initial lead came from a Discord message. Following it through the application and its f parameter exposed a command injection issue, which the agency later confirmed it had patched.
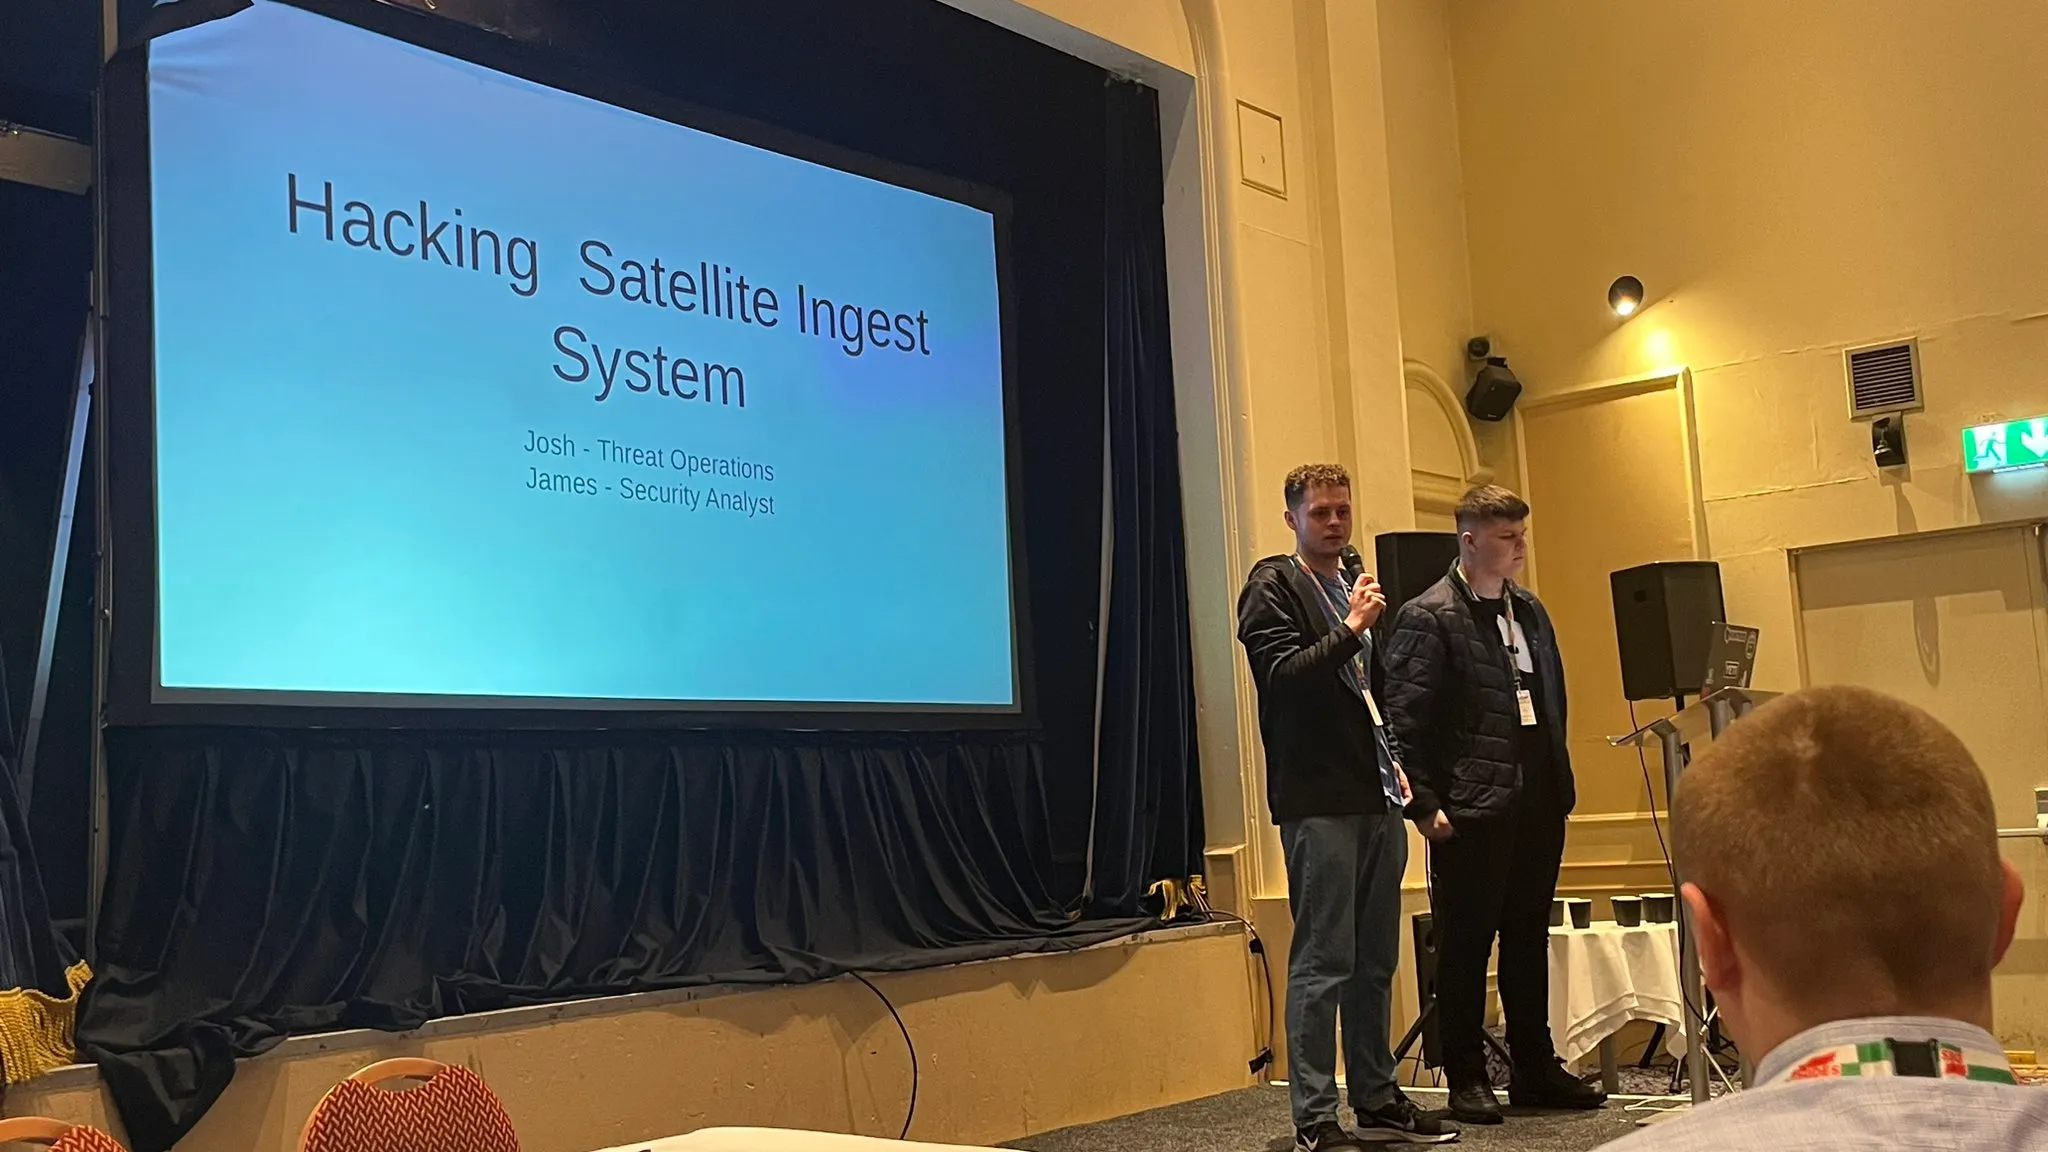
Kudos to @0SPwn (James W.) and @xorjosh (Josh Allman).
We presented the research at BSides Cymru 2023, including the discovery and disclosure process.